The Cybersecurity Toolkit Small Businesses Actually Need (and What You Can Skip)
You don't need an enterprise security stack. You need five controls done properly: MFA, a password manager, updates, backups and phishing awareness. Here's how to set them up.
Key takeaways
- Five controls stop most attacks on small businesses: MFA, a password manager, automatic updates, tested backups and phishing awareness.
- Turn on multi-factor authentication for email, banking and admin accounts first — this week.
- Backups only count if you have restored from them at least once.
- Skip expensive 'enterprise' tools until the basics are in place and owned by a named person.
Small businesses are attractive targets precisely because they're less defended. Attackers rarely "hack" in the movie sense; they log in with a stolen password, trick someone into paying a fake invoice, or encrypt files that were never backed up. The good news is that a short list of well-implemented basics blocks most of these attacks — and most of them cost little or nothing.
This guide covers the essential toolkit, in the order to implement it, and the things you can safely postpone.
The five controls that matter most
Public guidance for small businesses from agencies such as CISA, the FTC and NIST keeps landing on the same fundamentals. If you do nothing else, do these:
| Control | What it stops | Typical cost | Owner effort |
|---|---|---|---|
| Multi-factor authentication (MFA) | Account takeover from stolen or guessed passwords | Usually free (built into email, banking, SaaS) | Low |
| Password manager | Reused and weak passwords; insecure sharing | Low per-user monthly fee | Medium (rollout) |
| Automatic updates | Attacks on known software vulnerabilities | Free | Low |
| Backups (tested) | Ransomware, accidental deletion, hardware failure | Low to moderate | Medium |
| Phishing awareness | Fake invoices, credential theft, payment fraud | Free to low | Low, ongoing |
1. Turn on multi-factor authentication — starting with email
Your email account is the master key: whoever controls it can reset passwords for nearly everything else. Turn on MFA in this order:
- Email (Google Workspace, Microsoft 365 or your provider).
- Banking and payment accounts.
- Domain registrar and DNS — losing your domain means losing your email and website.
- Admin accounts for your website, accounting, payroll and CRM.
- Everything else that offers it.
Prefer an authenticator app or security key over text-message codes where possible; SMS is better than nothing but can be intercepted through SIM-swap fraud. For admins, a hardware security key is inexpensive and very effective against phishing.
2. Roll out a password manager
Password reuse is the single biggest reason a breach at some unrelated website turns into a breach of your business. A business password manager lets every employee use long, unique passwords and lets you share logins securely instead of sending them over chat or a spreadsheet.
What to look for: shared vaults or collections, admin recovery, the ability to remove access when someone leaves, and reporting on weak or reused passwords. We cover this in detail in our password manager guide.
3. Make updates automatic
Most successful attacks use vulnerabilities that already have a fix. Turn on automatic updates for:
- Operating systems on every laptop and phone.
- Browsers (they usually update themselves — just make sure people restart them).
- Your website platform and its plugins, if you run WordPress or similar.
- Routers and firewalls, which are often forgotten for years.
Replace devices that no longer receive security updates. An old laptop running an unsupported operating system is a liability, not a bargain.
4. Back up — and test the restore
Ransomware works because victims can't get their data back any other way. Follow the 3-2-1 rule: three copies of your data, on two different types of storage, with one copy off-site (usually the cloud). Crucially, keep at least one copy that ransomware can't reach — an immutable or versioned cloud backup, or a disconnected drive.
Don't forget SaaS data. Google Workspace and Microsoft 365 keep your files available, but they're not a full backup service; deleted items eventually disappear. Our cloud backup guide explains the options.
5. Teach people to spot phishing and payment fraud
Most incidents in small businesses start with a message: a fake invoice, a "CEO" asking for gift cards, a supplier "changing bank details," a login page that looks like Microsoft. Short, regular reminders beat an annual training slideshow.
Make these rules explicit:
- Any change of bank details is confirmed by phone using a number you already have — never the one in the email.
- Urgency is a red flag. Real executives can wait ten minutes for a verification call.
- Report, don't delete. Make it easy and blame-free to forward suspicious messages to one person.
- Never approve an MFA prompt you didn't trigger.
Who owns security?
In a small business, security fails when it's everyone's job and therefore no one's. Name one person — an owner, office manager or trusted IT contractor — who:
- Keeps a list of the company's accounts and who has admin access.
- Removes access the same day someone leaves.
- Checks backups and updates monthly.
- Is the person staff contact when something looks wrong.
What you can skip (for now)
Vendors will happily sell a 15-person company an enterprise stack. Until the five basics are done, you can usually postpone:
- SIEM and log-analysis platforms — powerful, but they need someone to watch them.
- Expensive "next-gen" firewalls for a small office that mostly uses cloud apps.
- Penetration tests before you've fixed the obvious gaps; you'll pay to be told to turn on MFA.
Worth considering once the basics are in place: endpoint protection with central management (often included in business editions of Microsoft 365), device management for company laptops and phones, email security add-ons, and cyber insurance — whose application questionnaire is itself a handy checklist.
Have a one-page incident plan
When something goes wrong, people panic. Write down, on one page:
- Who to call first (internal owner, IT contractor, bank).
- How to disconnect an infected device from the network.
- How to reset passwords and revoke sessions in your email system.
- Where backups live and who can restore them.
- When to notify customers, your insurer and, where required, authorities.
Worked example: a 15-person accounting practice
Consider a hypothetical accounting firm with fifteen staff, Microsoft 365 email and a mix of laptops. A partner's mailbox was nearly taken over by a phishing email that imitated a document-sharing notice.
Week 1: the office manager is named security owner. MFA is turned on for every mailbox using an authenticator app, starting with partners and the admin account. A hardware key is issued to the two administrators.
Week 2: a business password manager is rolled out. Shared logins for the tax portals, bank and software vendors move into team vaults; the old spreadsheet is deleted.
Week 3: automatic updates are verified on every laptop; two machines too old for current security updates are replaced. A cloud backup service is added for mailboxes and OneDrive, and the first test restore is done.
Week 4: a 20-minute team session covers fake invoices and the new rule: any bank-detail change is confirmed by phone.
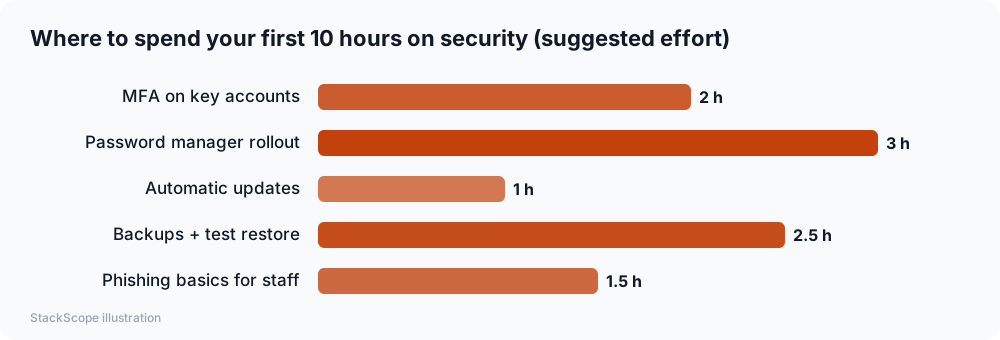
Result: about ten hours of work and a small monthly cost. When a supplier "changed bank details" by email two months later, the call-back rule caught it before any money moved.
Frequently asked questions
Is free antivirus enough? Modern operating systems include capable built-in protection. For a business, the bigger wins are MFA, updates and backups. Centrally managed endpoint protection becomes worthwhile as you grow.
We only use cloud apps. Do we still need backups? Yes. Cloud providers protect against their own failures, not against an employee deleting a folder, a compromised account wiping data, or a sync spreading ransomware-encrypted files.
How often should we review this? A quick monthly check (new accounts, departures, backups) and a deeper review once a year or after any incident.
The bottom line
Security for a small business is mostly discipline, not products: MFA everywhere, a password manager, automatic updates, tested backups and staff who know to pick up the phone before paying a changed invoice. Do those five well and you're ahead of most targets attackers see.